
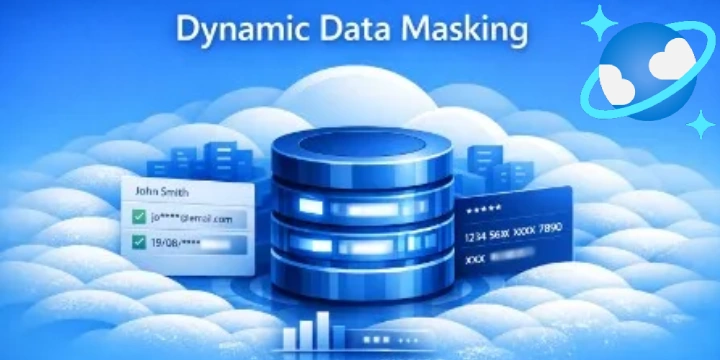
Microsoft has officially announced the general availability (GA) of Dynamic Data Masking (DDM) for Azure Cosmos DB for NoSQL. This security feature provides a centralized, policy-based method to protect sensitive data (such as PII or PHI) by automatically masking fields in query results for non-privileged users, without requiring any modifications to application code or the underlying data storage.
Key Benefits of Dynamic Data Masking
Server-Side Enforcement: DDM applies masking at query execution time. Privileged users retain access to full, unmasked values, while non-privileged users see masked results based on configured policies.
No Application Code Changes: Because masking is enforced within the database layer, developers don't need to implement conditional logic or custom masking functions within their applications.
Role-Aware Security: Leveraging Azure Cosmos DB’s role-based access control (RBAC), organizations can define who has permission to "unmask" data, simplifying the enforcement of least-privilege access.
Improved Compliance: DDM helps organizations meet strict data privacy requirements by limiting the exposure of sensitive information across diverse environments, support teams, and analytics workloads.
Supported Masking Strategies
The feature offers flexible strategies to handle different data types:
Default: Replaces string values with
XXXX, numeric values with0, and boolean values withfalse.Custom String: Uses
MaskSubstring(Start, Length)to mask specific portions of a string while keeping others visible.Email: Intelligently masks email addresses, showing only the first letter of the username and the domain extension (e.g.,
[email protected]).
Configuration and Implementation
DDM is configured through the Azure portal:
Enable Feature: Activate DDM in the "Features" tab under Settings.
Define Roles: Use RBAC to assign permissions, distinguishing between privileged users who can view raw data and standard users who receive masked results.
Apply Policies: Configure a masking policy at the container level using a JSON-based policy structure that defines
includedPaths(fields to mask) andexcludedPaths(fields to leave unmasked).
This update is a significant win for enterprise-grade security. It removes the operational burden of managing data visibility in application code, ensuring that sensitive information remains secure throughout the entire data lifecycle. For more technical details and implementation guides, visit the official Azure Cosmos DB blog.
Join the conversation! Your thoughts help the community grow.