
Pre-requisite to understand this
Authentication vs authorization
Familiarity with SSO, Identity Providers (IdP), and Service Providers (SP)
Knowledge of roles, permissions, and user groups
Awareness of common SSO protocols:
SAML 2.0
OAuth 2.0
OpenID Connect (OIDC)
High-level understanding of JWT / SAML assertions
Basic idea of RBAC (Role-Based Access Control)
Introduction
Role mapping in SSO is the process of translating identity and authorization data provided by an Identity Provider (IdP) into application-specific roles within a Service Provider (SP). While SSO primarily handles authentication, role mapping bridges the gap between authentication and authorization by ensuring users receive the correct access level after login. This process enables centralized identity management while allowing applications to enforce their own access control rules.
What problem we can solve with this?
SSO role mapping solves the challenge of consistent, scalable, and secure authorization across multiple applications.
Problems addressed:
Avoids maintaining separate user-role databases per application
Eliminates manual role assignment after login
Enables centralized identity governance
Ensures least privilege access
Reduces authorization mismatches between systems
Simplifies user onboarding/offboarding
How to implement/use this?
Role mapping is implemented by aligning IdP-provided attributes(roles, groups, claims) with application-specific roles during the SSO authentication flow.
High-level steps:
Configure IdP to:
Authenticate users
Include role/group claims in the token or assertion
Define role-mapping rules in the application
Translate IdP roles → Application roles
Enforce authorization based on mapped roles
Common role-mapping strategies:
Direct mapping(IdP role == App role)
Group-based mapping
Attribute-based mapping
Rule-based mapping
Sequence Diagram (SSO Role Mapping Flow)
This sequence shows how role mapping occurs after authentication but before authorization.
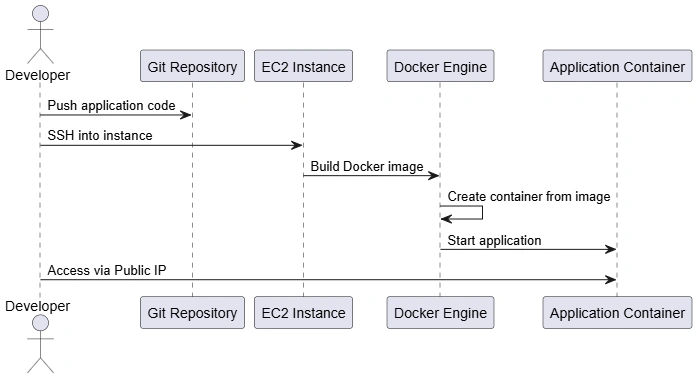
Key points:
The IdP is responsible for identity and role claims
The application never authenticates credentials directly
Role mapping occurs inside the Service Provider
Token validation ensures trust and integrity
Session creation includes mapped application roles
Component Diagram (Architecture View)
This diagram highlights logical responsibilities rather than runtime flow.
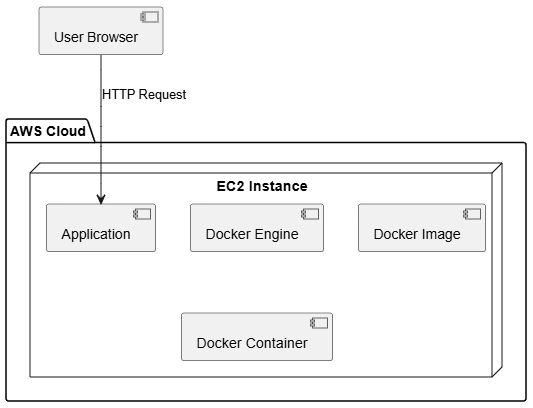
Identity Provider
Central authority for authentication
Sources roles from directory systems
Role Mapping Engine
Translates IdP roles/groups into application roles
Decouples IdP structure from app logic
Authorization Layer: Enforces access policies using mapped roles
Application remains independent of IdP internals
Advantages
Centralized identity and role governance
Reduced administrative overhead
Improved security posture
Consistent authorization across applications
Scalable for enterprise environments
Easier compliance and auditing
Faster user provisioning and deprovisioning
Decouples authentication from authorization logic
Summary
Mapping roles for SSO is a critical architectural pattern that enables applications to leverage centralized identity systems while maintaining fine-grained authorization control. By extracting role or group information from SSO tokens and translating them into application-specific roles, organizations achieve scalability, security, and consistency across systems. Proper role mapping ensures that authentication is seamless, authorization is precise, and applications remain flexible as identity systems evolve.
Join the conversation! Your thoughts help the community grow.