
This series of articles, based on my previous working notes, discusses the main feature of the application security protection. The procedure is a security checking automation to figure out the potential security issues and give the developer a chance to fix them. My previous Security series of articles, such as Example Of Cross-Site Scripting, Reflected, was based on the security scanning tools to detect issues and to indicate the possible security vulnerabilities and solutions.
- Application Security (1), in General --- this article
- Application Security (2), Static Code Scanning --- Fortify
- Application Security (3), Open Source Security --- Sonatype
- Application Security (4), Dynamic Web Scanning --- WebInspect
A - Introduction
This article will introduce Application Security in general and roughly discusses Fortify, Static Code Analysis (SCA), Sonatype, Open Source Security (OSS), WebInspect, and Dynamic Web App Scanning. The content of this article is
- A - Introduction
- B - Application Security
- B - 0 - AppSec Overview
- B - 1 - Secure Code Training --- Earliest Stage of Software Development
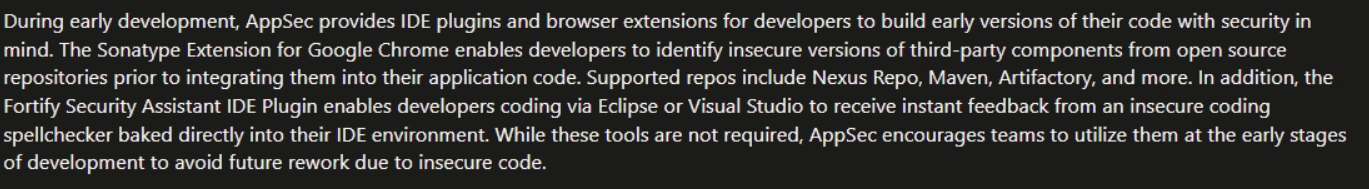
- B - 2 - Security Tools plugins --- Early Development
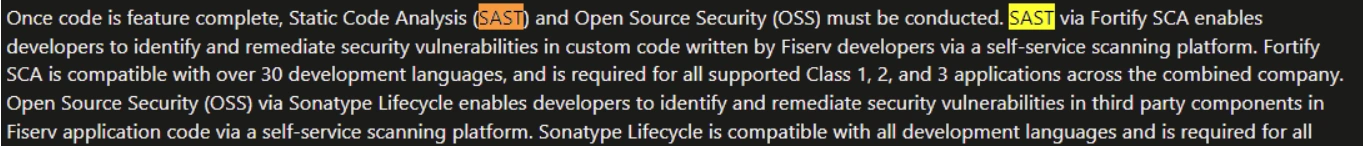
- B - 3 - Static Security Scanning --- after the code is completed
- B - 4 - Dynamic Security Scanning --- after code deployed
- B- 5 - MAST
- C - What is Fortify
- D - What is Sonatype
- E - What is WebInspect
- What is WebInspect?
- Who uses WebInspect?
- Why should we use WebInspect?
- Scope
B - Application Security
Here, we will describe the company Application Security process, although it is from one specific company, it might have generic sense for the process itself.
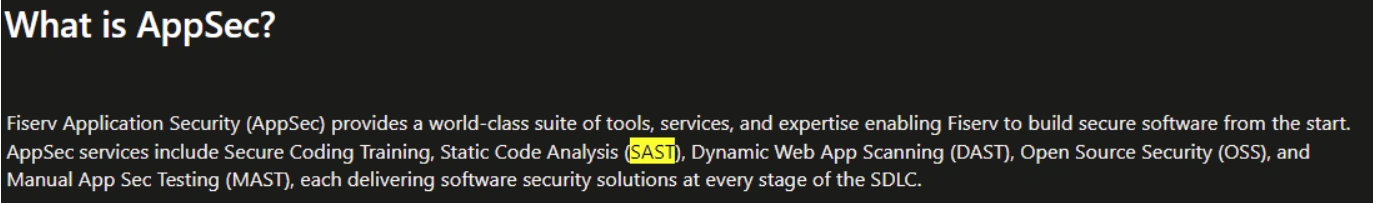
B - 0 - AppSec Overview
Company Application Security (AppSec) provides a world-class suite of tools, services, and expertise, enabling the Company to build secure software from the start. AppSec services include
- Secure Coding Training (SCT), Static Code Analysis (SCA), --- Fortify
- Static Code Analysis (SCA)
- Statice App Sec Testing (SAST)
- Dynamic Web App Scanning (DWAS), --- WebInspect
- Dynamic App Sec Testing (DAST)
- Open Source Security (OSS), --- Sonatype
- Manual App Sec Testing (MAST)
B - 1 - Secure Code Training --- Earliest Stage of Software Development
-
A Secure Code Training is offered during the earliest stage of software development.

B - 2 - Security Tools plugins --- Early Development:
- Sonatype Extension
- Fortify Security Assistant IDE Plugin
B - 3 - Static Security Scanning --- after the code is completed
- Statice Code Analysis (SCA) --- Fortify Scanning
- Open Source Security (OSS) --- SonaType
B - 4 - Dynamic Security Scanning --- after code deployed:
- WebInspect

B- 5 - MAST
- Manual Application Security Testing (MAST)

C - What is Fortify
- Static AppSec Testing (SAST) = Fortify
Fortify Scanning include
- Static Code Analysis (SCA ) --- Fortify
- Open Source Security (OSS) --- Sonatype
- Dynamic App Sec Testing (DAST) --- WebInspect
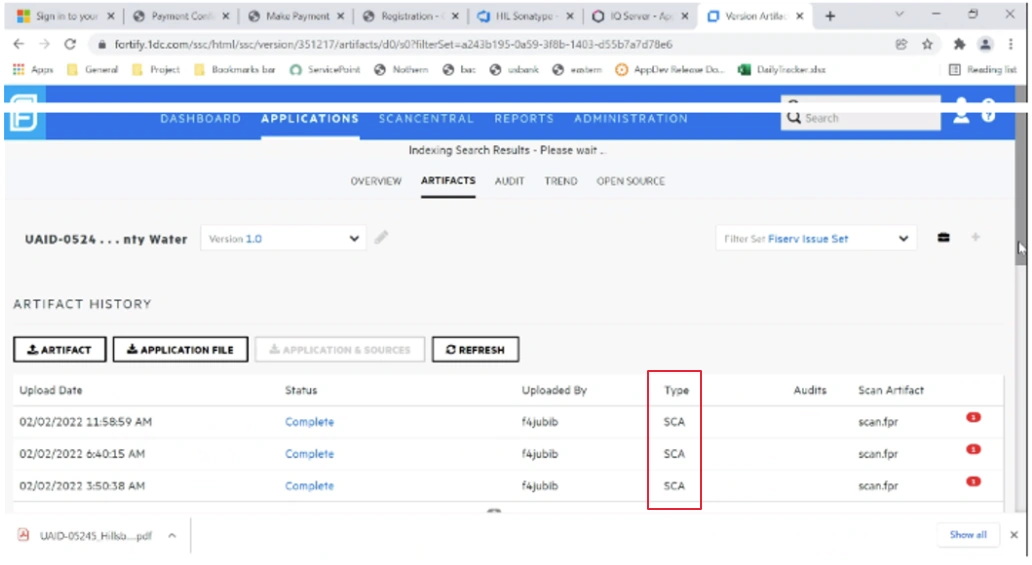
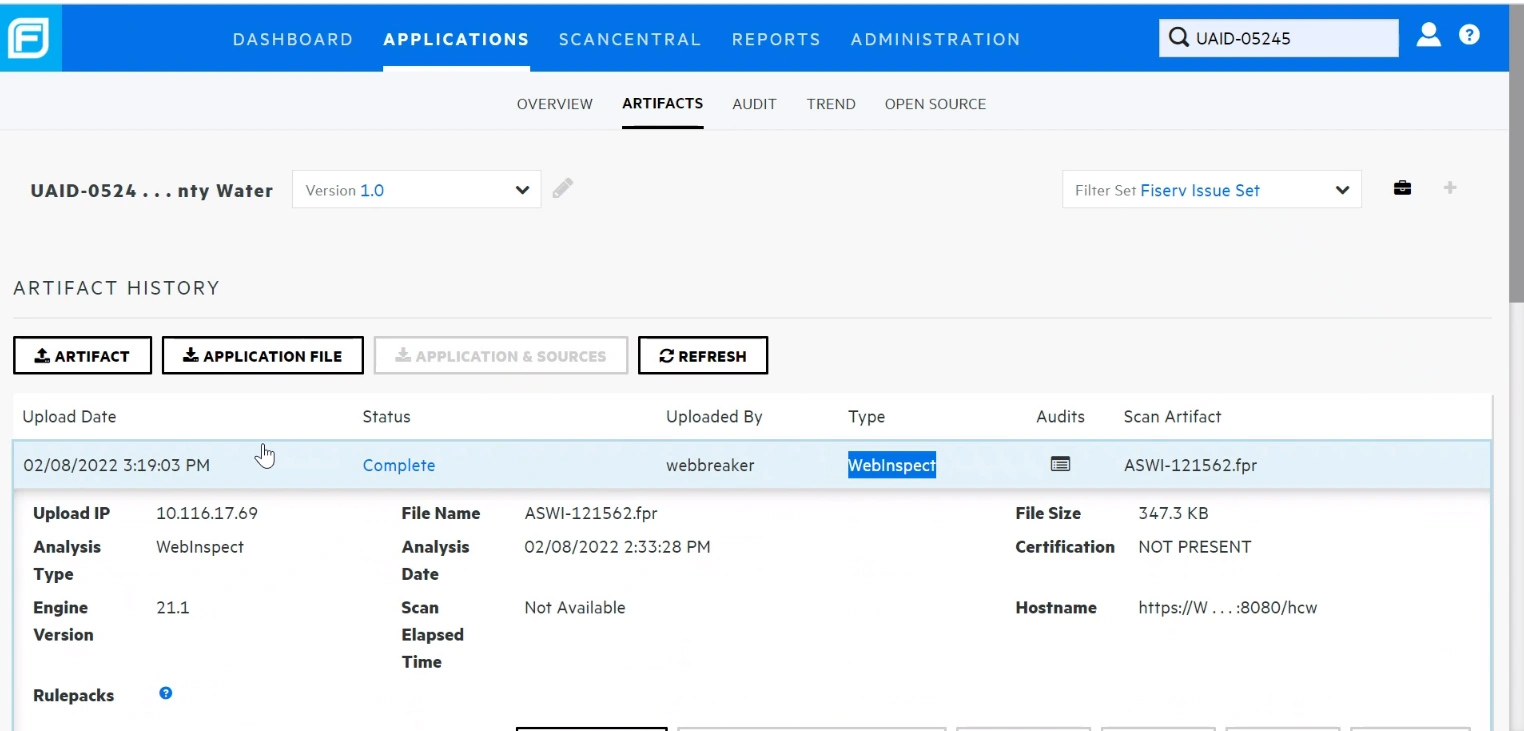
This is the scanning tool screen, the type could be SCA, OSS, or WebInspect (see the panel at the bottom of this article):
D - What is Sonatype
We will discuss the details in this article: Application Security (3), Open Source Security --- Sonatype
E - What is WebInspect
Dynamic AppSec Testing (DAST) = WebInspect
What is WebInspect?
- WebInspect is the industry-leading dynamic application security testing (DAST) tool for performing automated vulnerability assessments of of websites, web services, & APIs during DEV/QA testing early in SDLC.
Who uses WebInspect?
- WebInspect is provided by Cyber Security to all AppDev teams at the Company. All Class 1-3 applications are required to use WebInspect to identify and address vulnerabilities prior to releasing code in production. Class 4 applications are encouraged by WebInspect to enhance the security posture of their applications.
Why should we use WebInspect?
- Rather than waiting for manual security testing at the end of the SDLC, WebInspect enables AppDev teams to run self-service web app vulnerability scanning of any URL-based application during DEV/QA. With WebInspect, developers can find & fix vulnerabilities early in the SDLC, helping the Company build more secure, high-quality code faster than ever before.
Scope
- All applications with a web app (website), web service, and/or API component are in-scope for WebInspect (DAST).
References
Join the conversation! Your thoughts help the community grow.